
Available for Android
End-to-end encrypted chats from Europe — with post-quantum key exchange from the very first handshake.
- Channel
- MLS · RFC 9420
- Keys
- X-Wing · ML-KEM-768
- Mode
- End-to-end
- End-to-end encrypted
- X-Wing · ML-KEM-768
- No phone number
- No ads
- No tracking
- Made in Europe
01The route of a message
Readable only at the two ends.
In between there is only noise — on our own server too.
Your device
See you tomorrow! I’ll bring cake.
Encrypted before it leaves
MLS (RFC 9420) with X-Wing: X25519 and ML-KEM-768 together. The keys are made on your device and stay there.
Silvra server
Encrypted data the server cannot read
Sees the content only as ciphertext
The server delivers, but holds no key. It cannot read the content — not even if a government asks.
Recipient’s device
See you tomorrow! I’ll bring cake.
Decrypted only at the end
Images, videos, voice messages and files each get their own AES-256-GCM key, which travels inside the MLS-encrypted message.
02The three pillars
Chat, Updates and points account. One app.
Chat
One-to-one and group conversations with images, voice messages, files and locations. Plus voice and video calls, and messages that delete themselves after an hour, a day or a week.
Updates
A feed for images and videos, visible only to your chat contacts. No public feed, no strangers, no reach metrics.
Points account
An optional, self-custodied points account — secured by a 24-word recovery phrase, sending only after biometrics or the device PIN. Without setting it up, it simply is not there.
03Features
Everything a messenger has to do.
Plus features that work without analysing your data.
Files and locations
Each file with its own AES-256-GCM key, locations in the same chat.
Voice and video calls
Encrypted over WebRTC (DTLS-SRTP), with classical schemes.
Disappearing messages
After an hour, a day or a week — your choice.
Polls and events
Groups with votes and shared events.
Reactions and forwarding
React to messages, forward them or star them for later.
Voice messages as text
Recognition runs on the device only — the recording never leaves it for that.
Groups with roles
Admins manage members; new members do not see old messages.
German and English
The app follows the device language or your choice.
App lock
With biometrics or the device PIN — even if someone holds your unlocked smartphone.
Devices and sessions
See where you are signed in, and sign devices out one by one.
Sign in with an email code
No phone number, no password: a six-digit code is enough.
Status
Available, on holiday, do not disturb — with an expiry if you like.
04Post-quantum by design
Encrypted against tomorrow’s adversary
Almost every messenger encrypts today. What matters is whether that encryption will also hold against a future quantum computer.
Methods common today rest on mathematical problems a sufficiently large quantum computer can solve. Nobody knows when such machines will exist — but keeping intercepted data until they do is already common practice.
Silvra therefore combines classical cryptography with ML-KEM, the method standardised in 2024 by the US standards institute NIST. Both together, not one alone: if one breaks, the other still holds.
- Protocol
- MLS · RFC 9420 (OpenMLS)
- Ciphersuite
- MLS_256_XWING_CHACHA20POLY1305_SHA256_Ed25519
- Key exchange
- X-Wing = X25519 + ML-KEM-768
- Signatures
- Ed25519 (classical)
- Messages
- ChaCha20-Poly1305
- Attachments
- AES-256-GCM, one key per file
- Implementation
- libcrux (Cryspen, formally verified)
If one breaks, the other holds.
The keys live only on your devices. We cannot read the content of your chats — not even if a government asks. What our servers can read includes posts in the Updates feed, your email address, your status, your signed-in devices, your group memberships and the connection data needed for delivery.
05Live demo · WebCrypto
Encryption, live in your browser
Type a message: it is encrypted right here with AES-256-GCM and decrypted straight back. The key is generated at random when the page loads, every encryption gets a fresh nonce — and none of it leaves your browser.
- Key · AES-256
- …
- Nonce
- —
- Ciphertext
- —
Type something — it is encrypted instantly.
A demo using AES-GCM in your browser. Silvra Messenger itself uses MLS with X-Wing (X25519 + ML-KEM-768).
06The app
Ready in two steps.
No password, no phone number, no settings you have to study first.
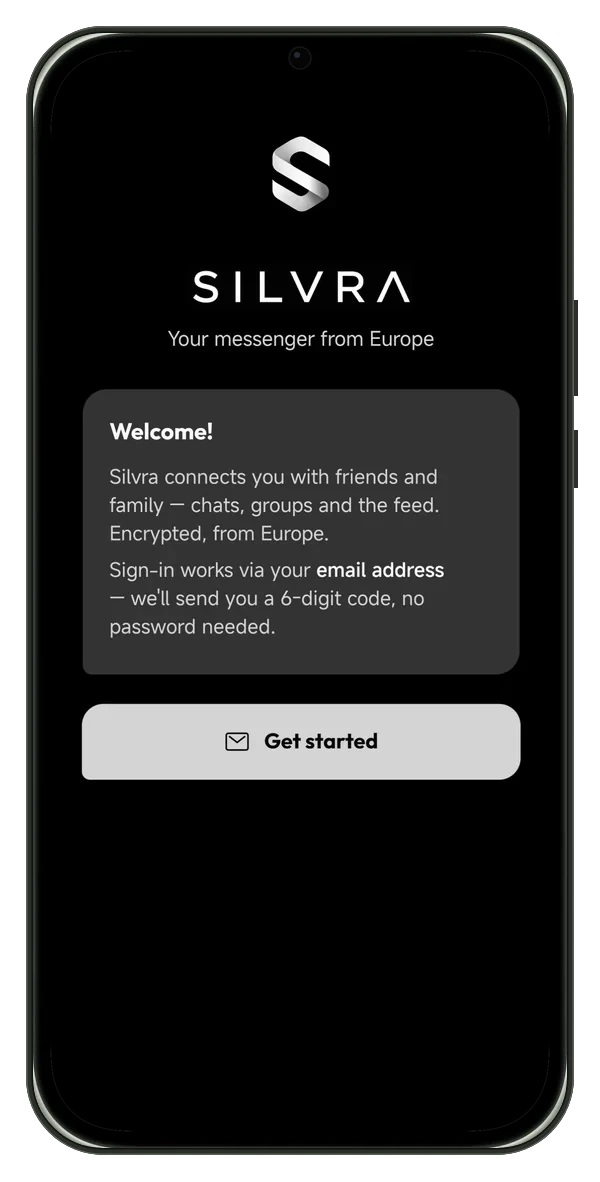
Sign in
Enter your email, confirm the code, done.
You get a six-digit code by email — no password to remember, no phone number in strangers’ address books.
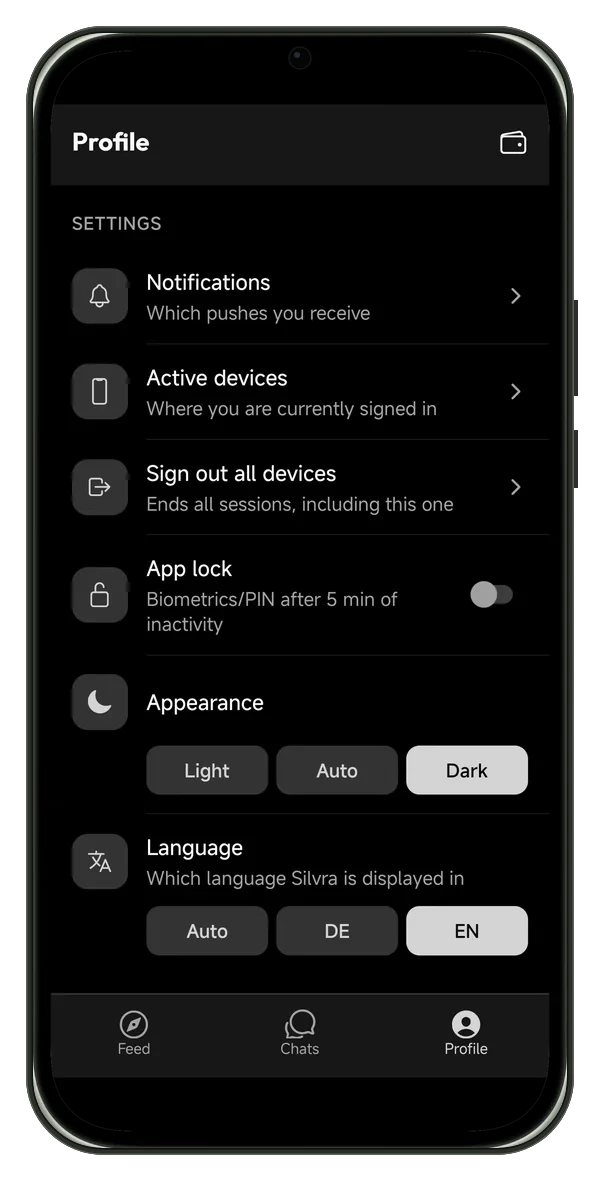
Settings
Everything that matters in one place.
Notifications, signed-in devices, app lock, appearance and language — clear, without nested submenus.
07Transparency
What is encrypted — and what is not
Every part of the app with the protection it actually has.
End-to-end encrypted
- Text in one-to-one and group chatsVia MLS (RFC 9420), hybrid with ML-KEM.
- Images, voice messages, files and locationsEach file with its own AES-256-GCM key, which travels inside the MLS-encrypted message.
Classical, not end-to-end, or limited by design
- Voice and video callsRun over WebRTC with DTLS-SRTP — encrypted, but with classical methods.
- Sender signaturesEd25519 — a classical scheme. Recorded messages stay protected by X-Wing; a future quantum computer could, however, forge signatures and actively insert itself into a group.
- Posts in the Updates feedNot end-to-end encrypted: posts are stored in plain text on the server.
- Old messages on a new deviceA newly signed-in device cannot read past encrypted messages. This follows from the protocol: a new device joins an MLS group only from the moment it is added and receives no keys for earlier epochs.
08Scope
What the messenger is not
Not an ad network
There is no business model that sells data. Accordingly no ad space and no tracking.
Not a crypto exchange
No trading, no conversion to euros, no custody.
Not a phone-number network
Sign in with an email address and a six-digit code. No password, no number in anyone else’s address book.
Not open source
The messenger’s source code is not public at this time. Its building blocks are open: OpenMLS and libcrux.
09Questions
Questions about the messenger
Will I see old messages on a new device?
No. A newly signed-in device cannot read past encrypted messages. This follows from the protocol: a new device joins an MLS group only from the moment it is added and receives no keys for earlier epochs.
Are images and voice messages encrypted too?
Yes. Every file gets its own AES-256-GCM key; only the ciphertext is uploaded, and the key travels inside the MLS-encrypted message.
Are calls post-quantum secure?
No. Voice and video calls run over WebRTC with DTLS-SRTP — encrypted, but with classical schemes.
What is the points account?
An optional, self-custodied account secured by a 24-word recovery phrase only you know. Without setting it up, it is not there; sending needs biometrics or the device PIN.
What does the app cost?
Nothing. Silvra is free and ad-free.
10Download
Silvra Messenger for Android
Free on Google Play: end-to-end encrypted chats, encrypted calls, a feed for contacts only, groups and an optional points account — no ad networks, no selling of data.
Android for now · German and English
